HowTo

WordPress Security: 7 Essential Checks for a Safer Site
In this guide: A practical WordPress security checklist covering maintenance, accounts, protective controls, tested backups and incident readiness.
WordPress security depends on maintained software, protected accounts, appropriate hosting controls, and a workable recovery process. Vulnerabilities, stolen credentials, unsafe software and misconfiguration can all contribute to a compromise. No single plugin or setting removes every risk.
Use this checklist to lock down your site.
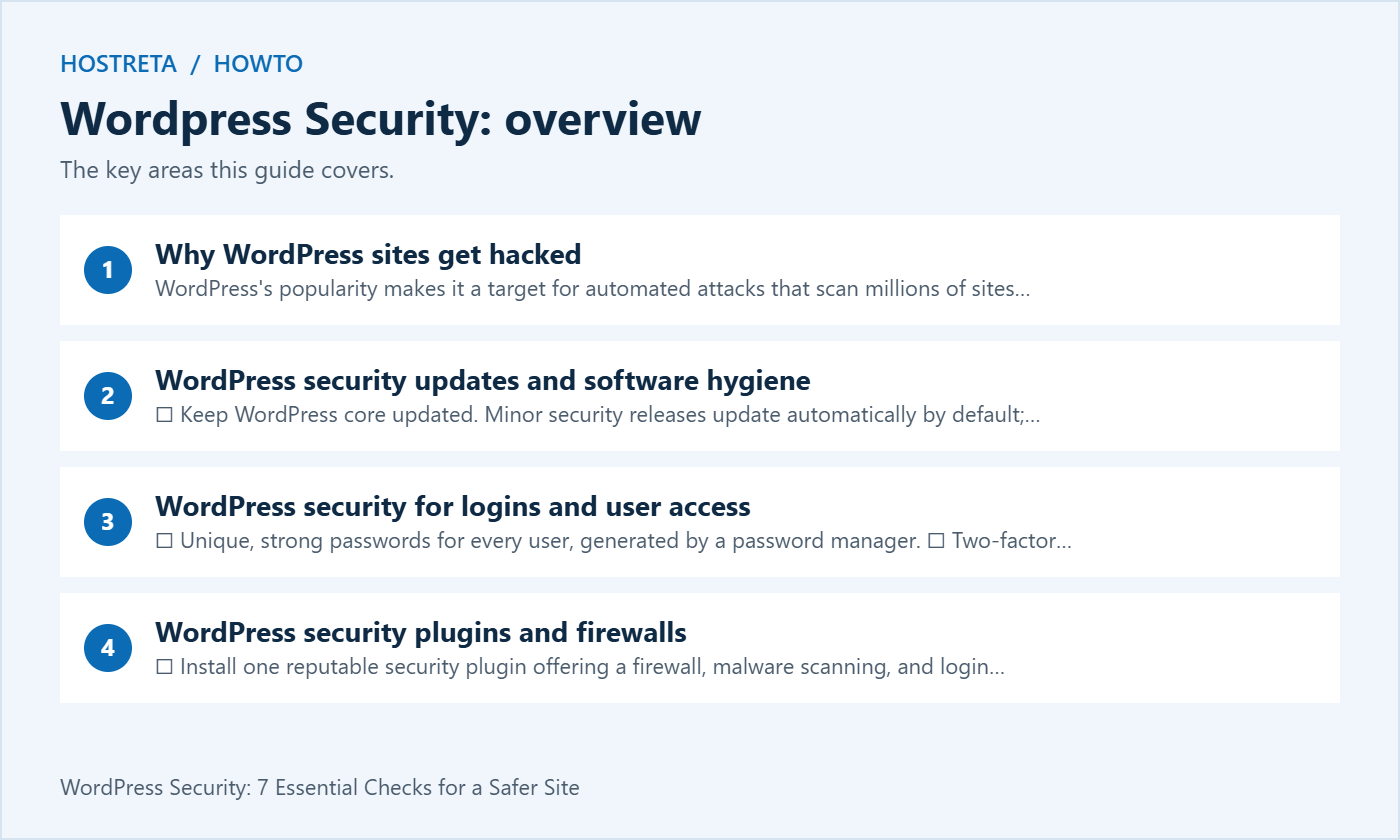
WordPress’s popularity makes it a target for automated attacks that scan millions of sites for known weaknesses. Common entry points:
Attackers usually aren’t targeting you specifically. They want server resources, SEO spam links, redirects, or a place to host phishing pages.
wp-config.php.☐ Disable file editing in the dashboard by adding to wp-config.php:
define( 'DISALLOW_FILE_EDIT', true );
☐ Force HTTPS across the entire site.
Strict-Transport-Security, X-Content-Type-Options, Referrer-Policy, and a well-tested Content Security Policy).Further reading: official WordPress documentation
A fast, well-supported host makes every WordPress task smoother. Kawedma WordPress hosting and managed WordPress hosting powered by Rocket.net include staging sites for safe testing, while shared hosting from Hosting.com or Kawedma shared hosting suit smaller sites. Protect the site with an SSL certificate and automatic backups from CodeGuard.
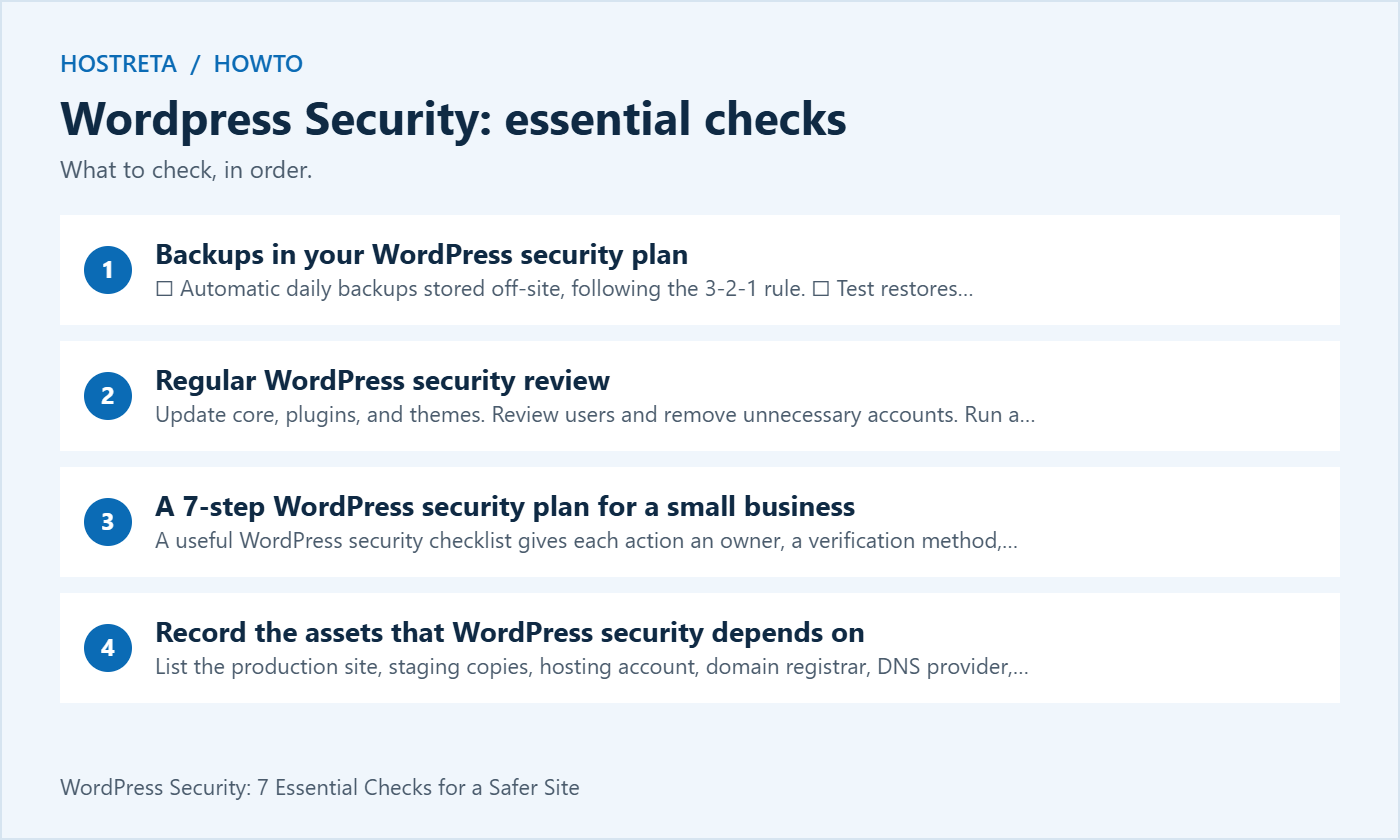
A useful WordPress security checklist gives each action an owner, a verification method, and a response when something fails. A list of installed plugins is not enough. Start by documenting what the website does, who administers it, where customer data is stored, and which external services can change the site. This inventory makes subsequent decisions more specific and easier to maintain.
The workflow below is for routine prevention and preparedness. If you already suspect an intrusion, use the incident section before making broad changes. Avoid deleting unknown files or replacing a live database while you are still trying to understand what happened. A recovery action can remove evidence or overwrite legitimate orders and enquiries if its scope is not clear.
List the production site, staging copies, hosting account, domain registrar, DNS provider, business email, backup storage, and administrative accounts. Include integrations that can publish content or deploy code. A WordPress security review that considers only the dashboard can overlook an exposed hosting account or a forgotten test site that still has access to sensitive information.
For each asset, record the owner and a safe recovery route. Store this information in an access-controlled place available to the people responsible for the website. Do not put credentials into a public document or ordinary website article. An inventory should help authorized people find the right account, not create another collection of unprotected passwords.
For example, a business may use an agency to build the website while retaining ownership of the domain and hosting. Document that division explicitly. The agency’s access should have a purpose and an expiry or review point. This is an operational example, not a claim that a particular division of responsibility is required for every organization.
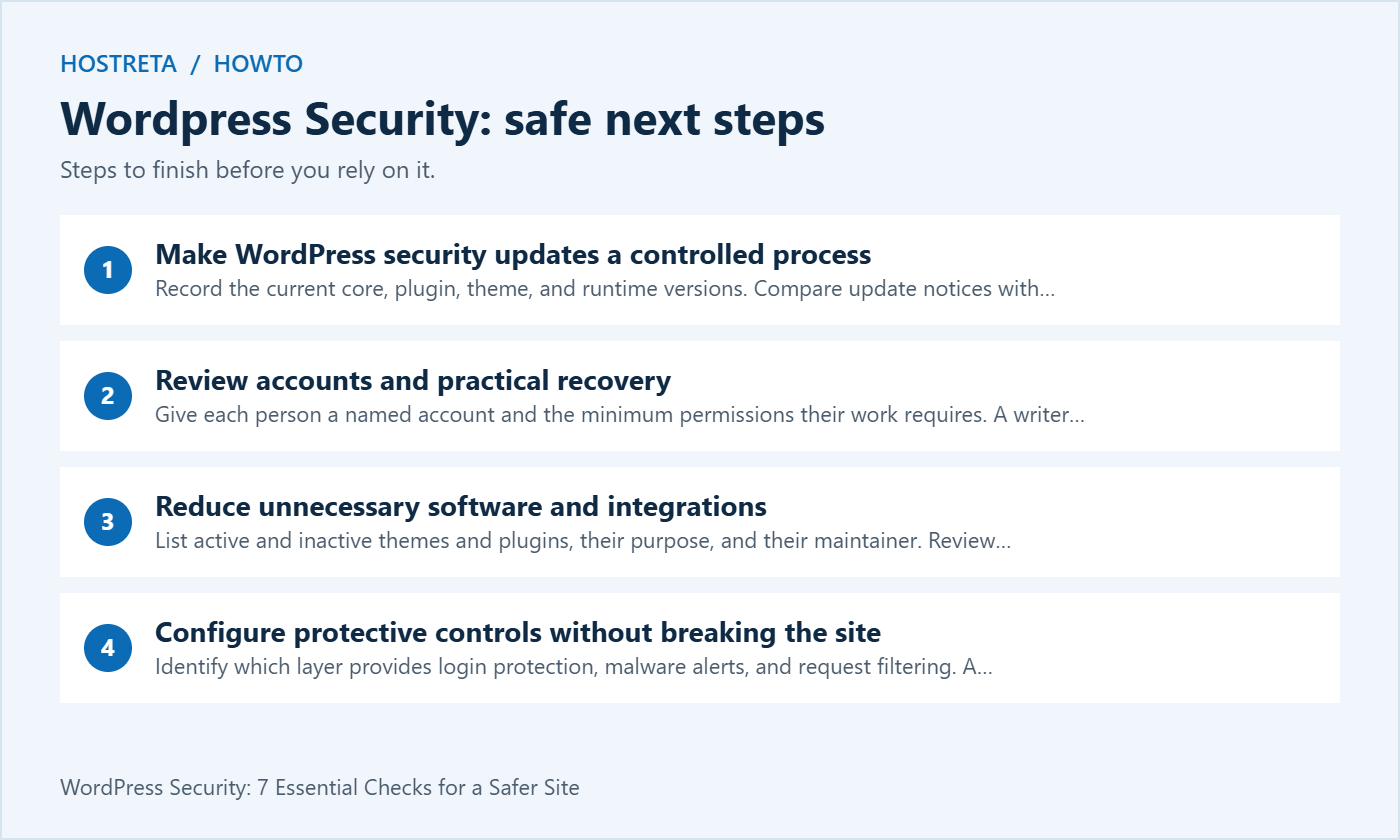
Record the current core, plugin, theme, and runtime versions. Compare update notices with the maintainers’ information and prioritize relevant security fixes. A maintenance routine should be frequent enough to handle urgent updates rather than waiting for a monthly calendar entry. On the other hand, pressing every available update button without a recovery plan can create an avoidable outage.
Before a significant change, confirm that you have a current backup and know how to restore it. Use a staging copy for compatibility checks where available. Test the functions that matter to the business: sign-in, navigation, forms, search, purchases, and email delivery. Keep the test focused on real workflows rather than checking only whether the homepage still loads.
Do not let staging become a permanent excuse for delaying a known security fix. If compatibility prevents an update, document the affected component and evaluate an alternative or a temporary reduction in exposure with qualified support. WordPress security maintenance needs both a way to apply changes and a way to resolve the cases where changes cannot be applied normally.
Give each person a named account and the minimum permissions their work requires. A writer who submits drafts normally does not need administrator privileges. Review old contractor accounts and integrations alongside staff access. Before changing or removing access, confirm who owns the account, whether it is still in use, and whether business content needs to be reassigned.
Use strong, unique credentials and a supported additional authentication method for privileged access. Keep recovery codes protected and verify the recovery process without deliberately locking out the only administrator. WordPress security improves when authentication is strong and recoverable. A setup that relies on one person’s unavailable phone can leave the business unable to maintain the site.
Protect the associated email account and domain account as well. Email often participates in password recovery, while DNS and hosting accounts can affect the website independently of WordPress. Evaluate these as connected parts of the same operating environment. Do not describe a changed login address as a substitute for authentication, timely updates, or appropriate permissions.
List active and inactive themes and plugins, their purpose, and their maintainer. Review abandoned or unused components and plan their removal through a reversible maintenance process. Keep the theme needed for the site’s actual configuration and any justified fallback arrangement. Do not delete files solely because their names are unfamiliar; investigate their source and role first.
Install software from trusted distribution channels and confirm that updates are still available. A premium license affects access to support and updates; it is not proof that software cannot contain a vulnerability. Similarly, a free plugin is not automatically unsafe. WordPress security decisions should consider maintenance, permissions, compatibility, and documented behavior instead of price alone.
Review integrations before disabling shared interfaces such as XML-RPC or the REST API. A site may rely on them for publishing, applications, or connected services. Check the dependencies and apply an appropriate control to the actual exposure. Blocking an interface without understanding its use can break legitimate operations while leaving unrelated entry points untouched.
Identify which layer provides login protection, malware alerts, and request filtering. A host, CDN, and WordPress plugin can all participate. Document their responsibilities so the team knows which dashboard to investigate. More products do not automatically mean stronger WordPress security, especially when overlapping rules create lockouts or make it hard to explain which control blocked a request.
Apply new firewall rules gradually and test important functions. A checkout callback, form submission, or administrative request may resemble traffic a generic rule tries to block. Keep a narrow, documented exception process instead of disabling the whole firewall when a false positive appears. Preserve evidence of the affected request without copying sensitive customer information into public support messages.
Use HTTPS consistently and investigate mixed-content or certificate problems. Advanced headers need testing and an understanding of the domains and embedded resources involved. For example, a restrictive content policy can break payment tools or embeds. HSTS has persistence and deployment implications, so establish reliable HTTPS coverage before choosing a broad policy.
Check what the backup actually contains, where it is stored, how long versions are retained, and who can restore it. A database copy alone does not necessarily include uploaded media, plugins, or configuration. A full collection of files without the corresponding database may also be insufficient. WordPress security planning should identify the components needed for a working recovery.
Choose a backup frequency according to how much recent activity the business can afford to lose. A small brochure site and a busy store have different recovery needs. Daily backups are not automatically sufficient for a site receiving frequent orders. Keep copies separate from the production environment and consider whether the same compromised account could delete both the site and its backups.
Test restoration in an isolated environment. Confirm that the site loads and that representative functions work. Prevent a test copy from sending live customer messages or processing real payments. Record the restore date, the backup used, the person who performed it, and any missing pieces. A successful backup notification is useful evidence of a job; a tested restore is evidence of recoverability.
Decide who receives security alerts and how urgent messages reach that person. Review alerts for unexplained administrators, unusual changes, malicious redirects, unexpected publishing, and repeated authentication failures. A scanner’s clean result does not prove that every part of a site is safe, but monitoring can help identify a reason to investigate before customers report a problem.
Keep records with an appropriate retention period and access control. Logs can contain IP addresses, identifiers, or request details, so avoid publishing them as ordinary article attachments. When asking for support, share the minimum relevant information through an appropriate channel. WordPress security monitoring should improve investigation without becoming another source of unnecessary data exposure.
Create a short escalation route naming the website owner, hosting support, technical maintainer, and any specialist incident help. Establish who can approve downtime and who communicates with customers. This is particularly valuable when a team spans time zones. Monitoring is only actionable when someone knows what to do with the alert.
| Control | Evidence | Review trigger |
|---|---|---|
| Software maintenance | Component inventory and last verified update | A security notice or planned release |
| Administrative access | Named owner, purpose and permission level | Staff or supplier changes |
| Backups | Scope, retention and isolated restore result | New business workflow or failed job |
| Firewall and alerts | Responsible layer and tested contact route | New integration or false positive |
| Incident readiness | Contacts and recovery decision process | A rehearsal or actual incident |
Use the table as a working record, not a public declaration that the site is perfectly secure. Mark unknown items as unknown and give them a follow-up owner. WordPress security benefits from honest gaps because they can be investigated. A completed-looking checklist with no supporting evidence can conceal exactly the dependency that matters during an outage.
First record what you observed and when: the affected URL, warning message, unexpected account, or suspicious redirect. Use a trusted device and established support channels. Contact the hosting provider or maintainer and preserve relevant evidence. The official WordPress hacked-site guidance is a useful reference for organizing the response.
Decide whether temporarily restricting the affected service is necessary to protect visitors. This decision should account for the site’s function and the evidence available. Do not simply hide a warning and continue taking customer information. If sensitive information might be involved, use appropriate professional advice about investigation and any obligations relevant to the business.
Plan recovery around a known clean state and the identified entry point. Restoring an older backup may remove visible damage while leaving the vulnerable component or compromised credential in place. Likewise, changing a password alone will not remove malicious files. Verify the relevant accounts, software, and integrations as part of the recovery plan rather than treating one cleanup action as a complete solution.
For stores and other frequently updated sites, consider legitimate activity since the last clean backup before overwriting data. An unplanned restore can lose orders or submissions. After recovery, retest important workflows and review monitoring. See our hacked WordPress recovery guide for the broader workflow, and use specialist help when the scope is uncertain.
Use automated notifications for events that require prompt attention, review backup failures and relevant update notices regularly, and schedule deeper access and restore reviews. The exact frequency depends on site activity and available support. WordPress security work should reflect actual business risk and the time needed to recover, rather than a promise that every website can be secured in a fixed number of minutes.
After a major integration change, revisit the checklist. A new payment provider, booking system, or automation can introduce additional accounts and dependencies. Update the inventory and monitoring route at the same time as the feature launch. This keeps maintenance aligned with the site that exists today instead of the simpler site the business had last year.
There is no universal winner for every hosting environment. Compare the protection you already receive, the specific features you need, support, resource use, and compatibility. Our WordPress security plugin comparison can help structure the shortlist. Test the chosen configuration instead of treating installation as proof of protection.
You can own routine inventory, account reviews, update checks, and backup verification if you understand the tools and have a recovery route. Escalate unexplained compromise, complex server changes, or uncertain data exposure to qualified support. Keeping a record of what you know and what remains uncertain helps both self-managed maintenance and professional assistance.
No universal setting is safe for every deployment. The values often mentioned in tutorials are starting points that depend on ownership, the web server, and the host’s configuration. Follow your hosting guidance and the official permissions documentation. Do not make files broadly writable to solve an unexplained update failure.
No. Backups support recovery, while maintenance, access control, and monitoring address other parts of WordPress security. Review the backup scope and test restoration. A service with frequent copies can still be unsuitable if its retention is too short or no one knows how to obtain a working restore when the dashboard is unavailable.
For maintained background, consult the WordPress security handbook, its hardening guidance, and the backup documentation. Use those references to check configuration decisions for your own environment. This article is a practical planning framework and does not represent a security audit of your site.
We may earn a commission on purchases made through these links, at no extra cost to you.
Don’t miss the chance to participate in the biggest giveaway of this year.